Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Splunk Updated SPLK-5002 Exam Questions and Answers by irha

Page: 5 / 7

Splunk SPLK-5002 Exam Overview :

Exam Name: Splunk Certified Cybersecurity Defense Engineer
Exam Code: SPLK-5002 Dumps
Vendor: Splunk Certification: Cybersecurity Defense Analyst
Questions: 105 Q&A's Shared By: irha
Question 20

An EDR tool was recently purchased and needs to be integrated into existing Splunk SOAR playbooks. Which actions are typically associated with this type of asset?

Options:

A.

Block device, remove email, detonate URL, get indicator

B.

Block hash, block process, quarantine device, get indicator

C.

Block URL, block subdomain, quarantine device, get indicator, detonate URL

D.

Block hash, reset user password, quarantine device, get indicator

Discussion
Question 21

What framework in Enterprise Security allows engineers to build detections using known malicious IOCs, comparing them to event logs to find suspicious behavior?

Options:

A.

Asset & Intelligence Framework

B.

Incident Management Framework

C.

Threat Intelligence Framework

D.

OSINT Framework

Discussion
Question 22

In a Risk-Based Alerting implementation with Splunk Enterprise Security, which of the following best describes a risk factor?

Options:

A.

A multiplier of risk that depends on the characteristics of the specific user or asset.

B.

An event that modifies risk based on the characteristics of the specific user or asset.

C.

A tool to enable risk data model acceleration.

D.

A SOAR action that is drawn from annotations.

Discussion
Peyton
Hey guys. Guess what? I passed my exam. Thanks a lot Cramkey, your provided information was relevant and reliable.
Coby Oct 9, 2026
Thanks for sharing your experience. I think I'll give Cramkey a try for my next exam.
Mylo
Excellent dumps with authentic information… I passed my exam with brilliant score.
Dominik Oct 12, 2026
That's amazing! I've been looking for good study material that will help me prepare for my upcoming certification exam. Now, I will try it.
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Oct 26, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Lois
I passed my exam with wonderful score. Their dumps are 100% valid and I felt confident during the exam.
Ernie Oct 26, 2026
Absolutely. The best part is, the answers in the dumps were correct. So, I felt confident and well-prepared for the exam.
Question 23

Below is an example of a Sysmon process create log. Which EventCode would be associated with this log entry?
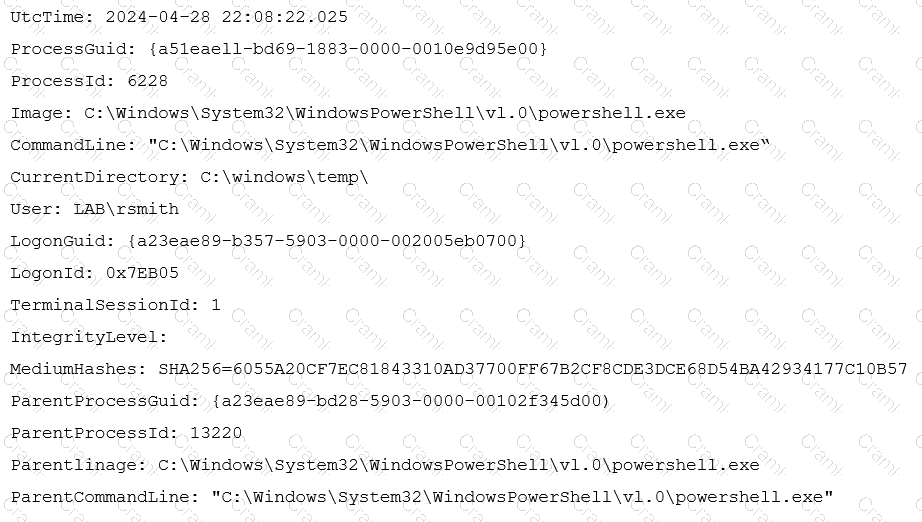

Questions 23

Options:

A.

EventCode=1

B.

EventCode=4

C.

EventCode=3

D.

EventCode=2

Discussion
Page: 5 / 7

SPLK-5002
PDF

$33  $109.99

SPLK-5002 Testing Engine

$39  $129.99

SPLK-5002 PDF + Testing Engine

$51  $169.99

