Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Page: 1 / 3

Application Security Certified Application Security Engineer (CASE) JAVA

Certified Application Security Engineer (CASE) JAVA

Last Update Nov 9, 2026
Total Questions : 47

To help you prepare for the 312-96 ECCouncil exam, we are offering free 312-96 ECCouncil exam questions. All you need to do is sign up, provide your details, and prepare with the free 312-96 practice questions. Once you have done that, you will have access to the entire pool of Certified Application Security Engineer (CASE) JAVA 312-96 test questions which will help you better prepare for the exam. Additionally, you can also find a range of Certified Application Security Engineer (CASE) JAVA resources online to help you better understand the topics covered on the exam, such as Certified Application Security Engineer (CASE) JAVA 312-96 video tutorials, blogs, study guides, and more. Additionally, you can also practice with realistic ECCouncil 312-96 exam simulations and get feedback on your progress. Finally, you can also share your progress with friends and family and get encouragement and support from them.

Questions 2

According to secure logging practices, programmers should ensure that logging processes are not disrupted by:

Options:

A.  

Catching incorrect exceptions

B.  

Multiple catching of incorrect exceptions

C.  

Re-throwing incorrect exceptions

D.  

Throwing incorrect exceptions

Discussion 0
Questions 3

A US-based ecommerce company has developed their website www.ec-sell.com to sell their products online. The website has a feature that allows their customer to search products based on the price. Recently, a bug bounty has discovered a security flaw in the Search page of the website, where he could see all products from the database table when he altered the website URL http://www.ec-sell.com/products.jsp?val=100 to http://www.ec-sell.com/products.jsp?val=200 OR '1'='1 -. The product.jsp page is vulnerable to

Options:

A.  

Session Hijacking attack

B.  

Cross Site Request Forgery attack

C.  

SQL Injection attack

D.  

Brute force attack

Discussion 0
Hassan
Highly Recommended Dumps… today I passed my exam! Same questions appear. I bought Full Access.
Kasper Oct 6, 2026
Hey wonderful….so same questions , sounds good. Planning to write this week, I will go for full access today.
Osian
Dumps are fantastic! I recently passed my certification exam using these dumps and I must say, they are 100% valid.
Azaan Oct 14, 2026
They are incredibly accurate and valid. I felt confident going into my exam because the dumps covered all the important topics and the questions were very similar to what I saw on the actual exam. The team of experts behind Cramkey Dumps make sure the information is relevant and up-to-date.
Joey
I highly recommend Cramkey Dumps to anyone preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Dexter Oct 26, 2026
Agreed. It's definitely worth checking out if you're looking for a comprehensive and reliable study resource.
Georgina
I used Cramkey Dumps to prepare for my recent exam and I have to say, they were a huge help.
Corey Oct 17, 2026
Really? How did they help you? I know these are the same questions appears in exam. I will give my try. But tell me if they also help in some training?
Questions 4

Which of the risk assessment model is used to rate the threats-based risk to the application during threat modeling process?

Options:

A.  

DREAD

B.  

SMART

C.  

STRIDE

D.  

RED

Discussion 0
Questions 5

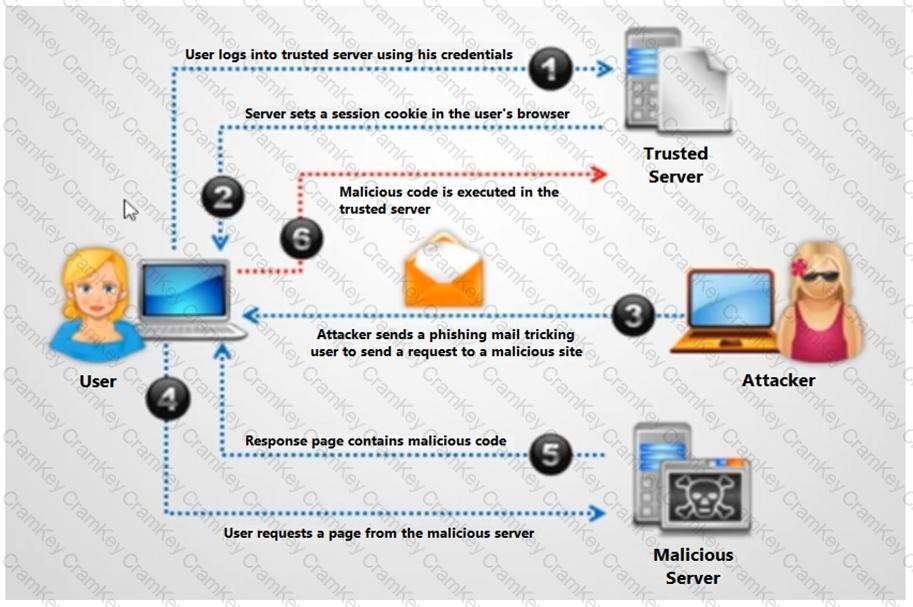
Identify the type of attack depicted in the figure below:

Questions 5

Options:

A.  

XSS

B.  

Cross-Site Request Forgery (CSRF) attack

C.  

SQL injection attack

D.  

Denial-of-Service attack

Discussion 0

312-96
PDF

$33  $109.99

312-96 Testing Engine

$39  $129.99

312-96 PDF + Testing Engine

$51  $169.99