Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

ECCouncil Updated 312-96 Exam Questions and Answers by mylah

Page: 3 / 3

ECCouncil 312-96 Exam Overview :

Exam Name: Certified Application Security Engineer (CASE) JAVA
Exam Code: 312-96 Dumps
Vendor: ECCouncil Certification: Application Security
Questions: 47 Q&A's Shared By: mylah
Question 12

Oliver, a Server Administrator (Tomcat), has set configuration in web.xml file as shown in the following screenshot. What is he trying to achieve?
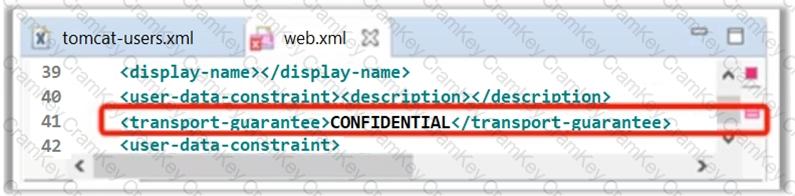
Questions 12

Options:

A.

He wants to transfer the entire data over encrypted channel

B.

He wants to transfer only response parameter data over encrypted channel

C.

He wants to transfer only request parameter data over encrypted channel

D.

He wants to transfer only Session cookies over encrypted channel

Discussion
Alessia
Amazing Dumps. Found almost all questions in actual exam whih I prepared from these valuable dumps. Recommended!!!!
Belle Oct 28, 2026
That's impressive. I've been struggling with finding good study material for my certification. Maybe I should give Cramkey Dumps a try.
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Oct 21, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Hassan
Highly Recommended Dumps… today I passed my exam! Same questions appear. I bought Full Access.
Kasper Oct 6, 2026
Hey wonderful….so same questions , sounds good. Planning to write this week, I will go for full access today.
Teddie
yes, I passed my exam with wonderful score, Accurate and valid dumps.
Isla-Rose Oct 28, 2026
Absolutely! The questions in the dumps were almost identical to the ones that appeared in the actual exam. I was able to answer almost all of them correctly.
Question 13

Which of the following Spring Security Framework configuration setting will ensure the protection from session fixation attacks by not allowing authenticated user to login again?

Options:

A.

session-fixation-protection ="newSessionlD"

B.

session-fixation-protection =".

C.

session-fixation-protection ="enabled"

D.

session-fixation-protection =".

Discussion
Question 14

Which of the following configurations can help you avoid displaying server names in server response header?

Options:

A.

< Connector port="8080" protocol="HTTP/1.1" connectionTimeout="20000" redirectPort= "8443" / >

B.

< Connector port="8080" protocol="HTTP/1.1" connectionTimeout="20000" ServerName=" disable" redirectPort="8443" / >

C.

< Connector port="8080" protocol="HTTP/1.1" connectionTimeout="20000" Server = " " redirectPort="8443" / >

D.

< Connector port="8080" protocol="HTTP/1.1" connectionTimeout="20000" ServerName ="null " redirectPort="8443'' / >

Discussion
Page: 3 / 3

312-96
PDF

$33  $109.99

312-96 Testing Engine

$39  $129.99

312-96 PDF + Testing Engine

$51  $169.99

