| Exam Name: | Fortinet NSE 5 - FortiSwitch 7.6 Administrator | ||
| Exam Code: | NSE5_FSW_AD-7.6 Dumps | ||
| Vendor: | Fortinet | Certification: | Fortinet Network Security Expert |
| Questions: | 114 Q&A's | Shared By: | griffin |
You are designing a multi-tenant network using FortiSwitch devices in standalone mode. Security is a priority and each tenant’s servers must be completely isolated from one another, and from all other servers in the network, to prevent lateral communication. However, all servers must have access to the shared FortiGate firewall for internet access. Which type of private VLAN (PVLAN) configuration should you apply to meet these security requirements? (Choose one answer)
Exhibit.
The exhibit shows the current status of the ports on the managed FortiSwitch.
Access-1.
Why would FortiGate display a serial number in the Native VLAN column associated with the port23 entry?
Refer to the exhibit.
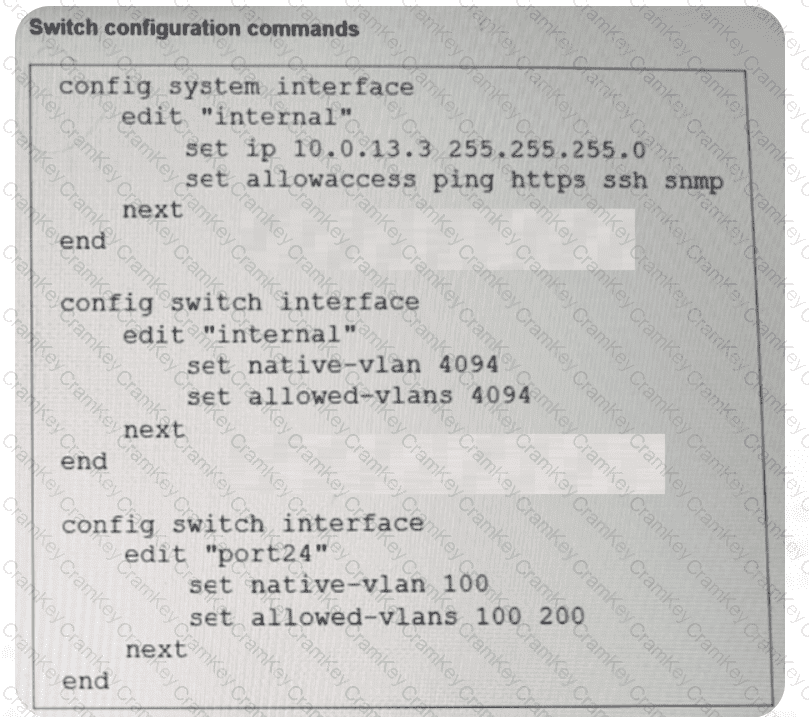
Port24 is the only uplink port connected to the network where you need access to FortiSwitch management services. However, FortiSwitch is not accessible on its management interface with IP address 10.0.13.3. Based on the configuration shown in the exhibit, which two actions should you take to fix the issue and access FortiSwitch? (Choose two answers)

TESTED 30 Sep 2026

