Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Juniper Updated JN0-336 Exam Questions and Answers by deen

Page: 4 / 4

Juniper JN0-336 Exam Overview :

Exam Name: Security, Specialist (JNCIS-SEC)
Exam Code: JN0-336 Dumps
Vendor: Juniper Certification: JNCIS-SEC
Questions: 68 Q&A's Shared By: deen
Question 16

What are two properties negotiated during IKE Phase 2? (Choose two.)

Options:

A.

routing protocol

B.

tunneling protocol

C.

aggressive mode

D.

Perfect Forward Secrecy

Discussion
Ari
Can anyone explain what are these exam dumps and how are they?
Ocean Oct 9, 2026
They're exam preparation materials that are designed to help you prepare for various certification exams. They provide you with up-to-date and accurate information to help you pass your exams.
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Oct 19, 2026
That sounds really useful. I'll definitely check it out.
Nia
Why are these Dumps so important for students these days?
Mary Oct 14, 2026
With the constantly changing technology and advancements in the industry, it's important for students to have access to accurate and valid study material. Cramkey Dumps provide just that. They are constantly updated to reflect the latest changes and ensure that the information is up-to-date.
Anya
I must say they're considered the best dumps available and the questions are very similar to what you'll see in the actual exam. Recommended!!!
Cassius Oct 14, 2026
Yes, they offer a 100% success guarantee. And many students who have used them have reported passing their exams with flying colors.
Question 17

You are deploying a new SRX Series device and you need to log denied traffic.

In this scenario, which two policy parameters are required to accomplish this task? (Choose two.)

Options:

A.

session-init

B.

session-close

C.

deny

D.

count

Discussion
Question 18

Which two statements are correct about IDP policy templates? (Choose two.)

Options:

A.

They are provided by Juniper Networks.

B.

They are not customizable.

C.

They are available on a “factory-default config.”

D.

They must be installed.

Discussion
Question 19

Which action will the SRX Series device take if traffic matches the custom attack object shown in the exhibit?
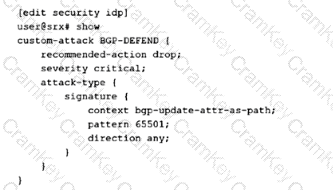

Questions 19

Options:

A.

the action taken is defined in the IDP policy that includes this attack object.

B.

the action taken is defined by the security policy.

C.

The SRX Series device will reject the traffic.

D.

The SRX series device will drop the traffic.

Discussion
Page: 4 / 4

JN0-336
PDF

$27.5  $109.99

JN0-336 Testing Engine

$32.5  $129.99

JN0-336 PDF + Testing Engine

$42.5  $169.99

