| Exam Name: | HPE Network Security Expert Written Exam | ||
| Exam Code: | HPE7-A10 Dumps | ||
| Vendor: | HP | Certification: | Aruba Certified Switching Expert |
| Questions: | 75 Q&A's | Shared By: | aylah |
A hospital uses an AOS-10 architecture managed by HPE Aruba Networking Central. The customer has deployed a pair of HPE Aruba Networking 9000 Series gateways, with Security licenses, at each clinic. The gateways run IDS/IPS in IDS mode.
The Security Dashboard displays several recent events with the same signature, as shown below:
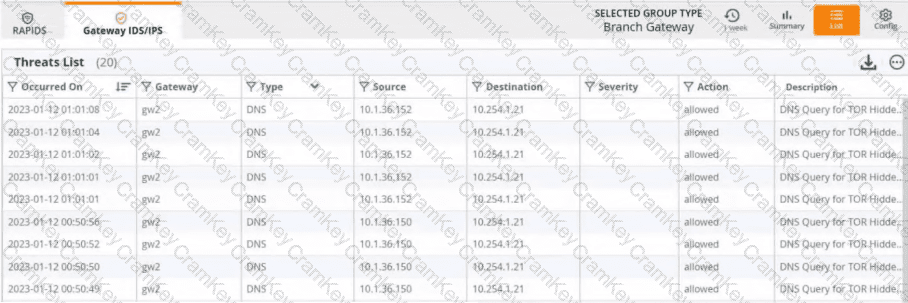
Occurred On: 2023-01-12 | Gateway: gw2 | Type: DNS | Source: 10.1.36.152 | Destination: 10.254.1.21 | Action: allowed | Description: DNS Query for TOR Hidden...
You want a record of the specific traffic that triggered the threat event. What should you do?
Customer introduction
You are assisting a company with adding HPE Aruba Networking ClearPass to its network, which uses HPE Aruba Networking infrastructure devices.
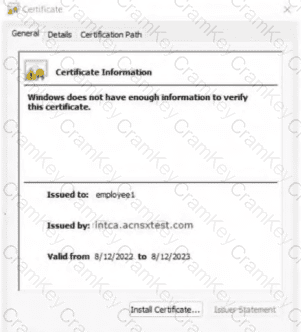
The company currently has a Windows domain and a Windows CA. The Windows CA issues certificates to domain computers, domain users, and servers such as domain controllers. An example certificate issued by the Windows CA is shown here.
ClearPass cluster IP addressing and hostnames
A customer's ClearPass cluster uses these IP addresses:
Publisher = 10.47.47.5
Subscriber 1 = 10.47.47.6
Subscriber 2 = 10.47.47.7
Virtual IP with Subscriber 1 and Subscriber 2 = 10.47.47.8
The customer’s DNS server has these entries:
cp.acnsxtest.com = 10.47.47.5
cps1.acnsxtest.com = 10.47.47.6
cps2.acnsxtest.com = 10.47.47.7
radius.acnsxtest.com = 10.47.47.8
onboard.acnsxtest.com = 10.47.47.8
Refer to the scenario.
The customer has now decided it needs CPPM to assign certain mobile-onboarded devices to a "nurse-call" AOS user role. These mobile-onboarded devices communicate with IP address 10.1.18.12 using port 4343.
What are the prerequisites for meeting this requirement?
A customer wants to avoid using RadSec between AOS-CX switches and ClearPass Policy Manager (CPPM) in order to reduce the need to manage switch certificates. Given this condition, what can you recommend to enhance security?
You are configuring gateway IDS/IPS settings in HPE Aruba Networking Central.
Why would you set the Fail Strategy to Bypass?

TESTED 16 Nov 2026

