| Exam Name: | Developing in Agentic AI Systems | ||
| Exam Code: | GH-600 Dumps | ||
| Vendor: | Microsoft | Certification: | GitHub Administrator |
| Questions: | 106 Q&A's | Shared By: | jaden |
You have a GitHub repository that contains the following custom agent files:
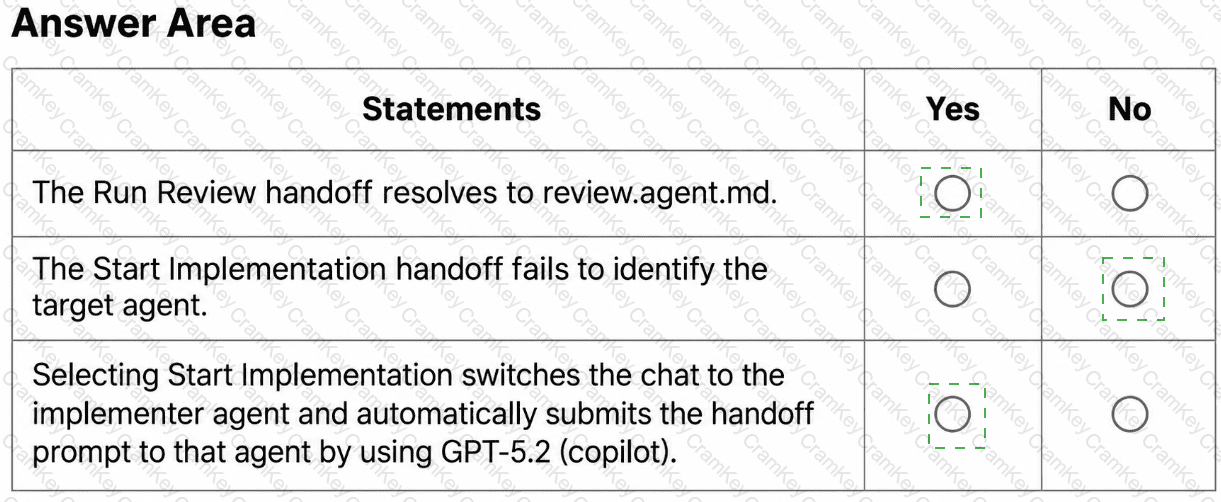
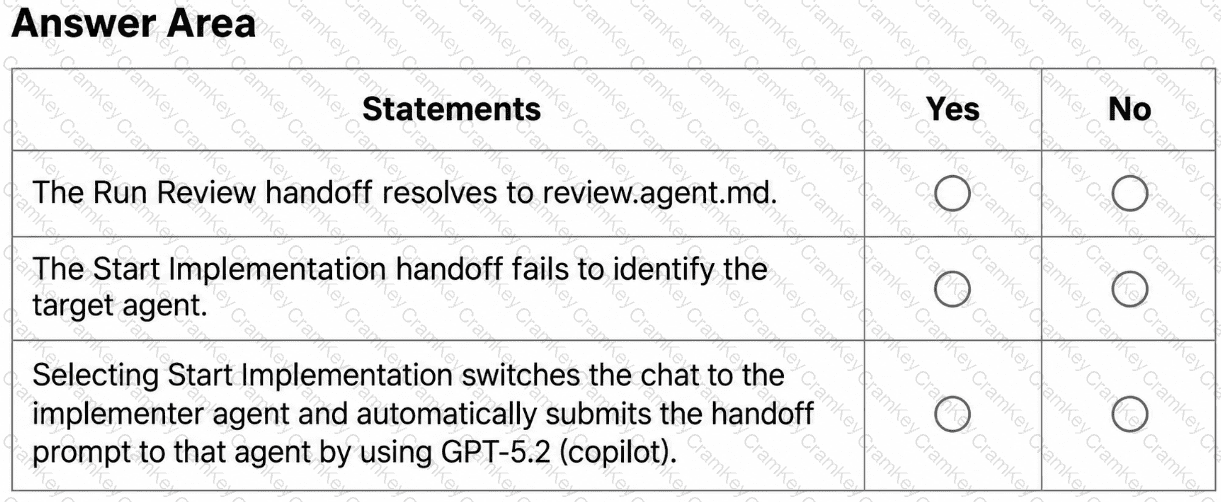
A file named planner.agent.md that includes YAML frontmatter with a handoffs entry that has label: Start Implementation, agent: implementer, and prompt: Now implement the plan outlined above.
A file named implementer.agent.md that is in the same directory as planner.agent.md and includes YAML frontmatter that has name: IMPLEMENTER.
You add a third agent file named review.agent.md that includes name: code-review in the YAML frontmatter.
You make the following changes to planner.agent.md:
Update the existing handoff to include send: true and model: GPT-5.2 (copilot).
Add a second handoff that has label: Run Review, agent: code-review, and prompt: Review the code changes made in the previous step.
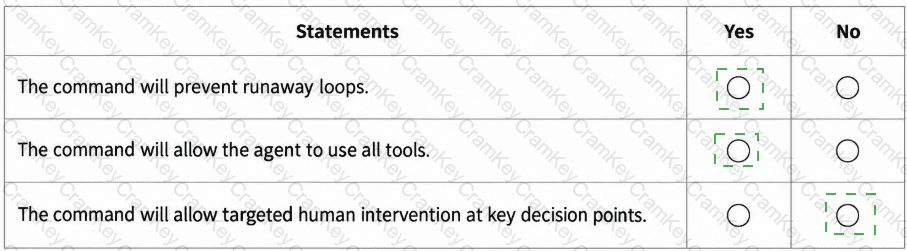
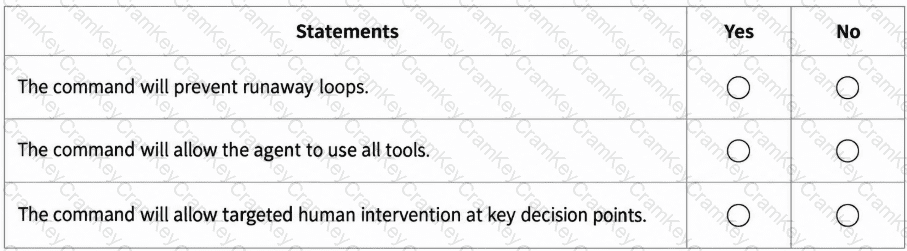
You have a GitHub repository that uses the following GitHub Copilot CLI command in a Bash script.
#!/usr/bin/env bash
set -euo pipefail
PROMPT= " Update dependencies, run tests, and open a pull request if changes are needed. "
copilot --autopilot --yolo --max-autopilot-continues 10 -p " $PROMPT "
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You have a GitHub Enterprise repository that runs an autonomous agent by using a GitHub Actions workflow. The workflow has the following jobs:
agent-run that generates trace.json and plan.md
review that waits for human approval before continuing
deploy that uses the outputs from agent-run
You need to make the files inspectable in the GitHub Actions UI and ensure that the files are available to the review and deploy jobs.
What should you do in the workflow?
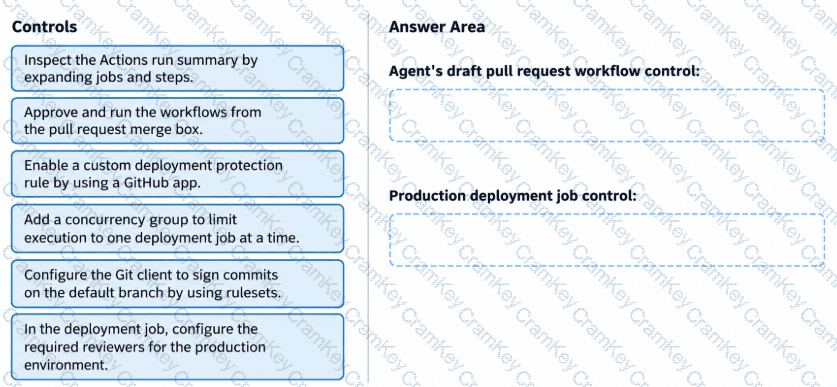
You have a GitHub Enterprise Cloud repository that uses the GitHub Copilot coding agent to resolve backlog issues by creating draft pull requests. The repository uses a GitHub Actions workflow for deployments to the production environment.
You discover that the workflow is being triggered before human review.
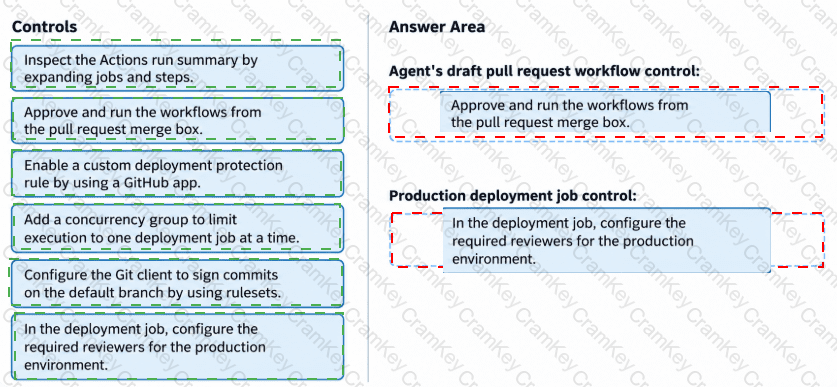
You need to configure GitHub controls to meet the following requirements:
The workflow for the agent’s draft pull requests must NOT run until a user that has write access approves the pull requests.
Production deployment jobs must start only after a user with write access explicitly approves the jobs.
Which controls should you configure? To answer, drag the appropriate controls to the correct requirements.

TESTED 22 Sep 2026