| Exam Name: | Microsoft Certified: Cloud and AI Security Engineer Associate | ||
| Exam Code: | SC-500 Dumps | ||
| Vendor: | Microsoft | Certification: | Microsoft Certified: Information Security Administrator Associate |
| Questions: | 224 Q&A's | Shared By: | beauden |
You have a Microsoft 365 tenant that has Microsoft 365 Copilot enabled for a pilot group.
Users frequently generate responses based on Microsoft Teams chats and Microsoft SharePoint Online sites.
You use Microsoft Purview Data Security Posture Management (DSPM) to identify inversharing risks and create policies based on the recommendations.
You need to manage and edit the policies created by DSPM
Which Microsoft Purview solution should you use?
You have an Azure subscription that contains the resources shown in the following table.
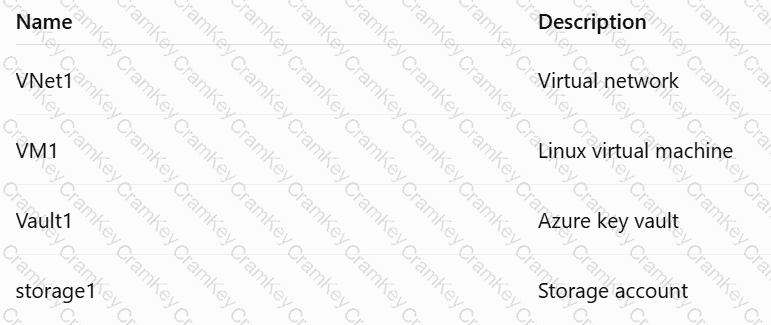
You plan to implement Microsoft Defender for Cloud.
Which resources can be protected by using Defender for Cloud?
You have a Microsoft Entra tenant that contains the users shown in the following table.
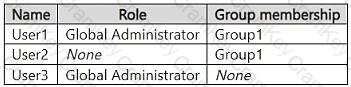
The tenant contains a Conditional Access policy named CA1 that has the following settings:
Assignments:
o Users or agents:
- Include: Directory roles: Global Administrator
Target resources:
o Resources (formerly cloud apps):
- Include: All resources
Conditions:
o Locations:
- Configure: Yes
- Include: Any network or location
Access controls:
o Grant:
- Require multifactor authentication
o Grant:
- Require device to be marked as compliant
o For multiple controls:
- Require all the selected controls
The tenant contains a Conditional Access policy named CA2 that has the following settings:
Assignments:
o Users or agents:
- Include: Users and groups: Group1
Target resources:
o Resources (formerly cloud apps)
- Include: Select resources: Office 365
Conditions:
o Locations:
- Configure: Yes
- Include: Any network or location
Access controls:
o Grant:
- Require multifactor authentication
o Grant:
- Require app protection policy
o For multiple controls:
- Require one of the selected controls
The users perform the following tasks:
User1 signs in to Microsoft 365 from a home network by using Microsoft Outlook on a noncompliant device.
User2 signs in to Microsoft 365 without an app protection policy by using a noncompliant device.
User3 signs in to the Azure portal from a home network by using a compliant device.
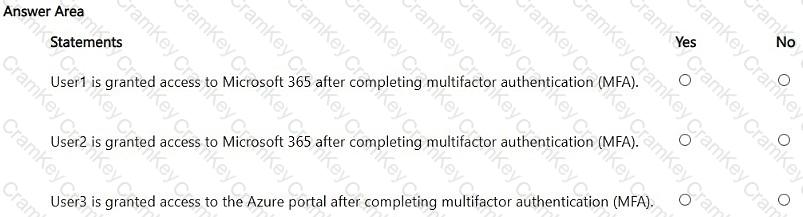
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
You have an Azure key vault named KV1.
You have an Azure App Service web app named App1. App1 is integrated with a virtual network named VNet1 that is linked to an Azure Private DNS zone. App1 accesses secrets stored in KV1.
You need to configure KV1 so that:
App1 accesses the secrets by using a private IP address on VNet1.
Requests from outside VNet1 are denied.
Which two actions should you perform? sc new

TESTED 03 Nov 2026


