Weekend Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Fortinet Updated NSE7_SDW-7.2 Exam Questions and Answers by elouise

Page: 5 / 7

Fortinet NSE7_SDW-7.2 Exam Overview :

Exam Name: Fortinet NSE 7 - SD-WAN 7.2
Exam Code: NSE7_SDW-7.2 Dumps
Vendor: Fortinet Certification: NSE 7 Network Security Architect
Questions: 99 Q&A's Shared By: elouise
Question 20

Which two statements describe how IPsec phase 1 main mode id different from aggressive mode when performing IKE negotiation? (Choose two.)

Options:

A.

A peer ID is included in the first packet from the initiator, along with suggested security policies.

B.

XAuth is enabled as an additional level of authentication, which requires a username and password.

C.

Three packets are exchanged between an initiator and a responder instead of six packets.

D.

The use of Diffie Hellman keys is limited by the responder and needs initiator acceptance.

Discussion
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Aug 1, 2026
That sounds really useful. I'll definitely check it out.
Mylo
Excellent dumps with authentic information… I passed my exam with brilliant score.
Dominik Aug 11, 2026
That's amazing! I've been looking for good study material that will help me prepare for my upcoming certification exam. Now, I will try it.
Carson
Yeah, definitely. I would definitely recommend Cramkey Dumps to anyone who is preparing for an exam.
Rufus Aug 7, 2026
Me too. They're a lifesaver!
Ayra
How these dumps are necessary for passing the certification exam?
Damian Aug 4, 2026
They give you a competitive edge and help you prepare better.
Anya
I must say they're considered the best dumps available and the questions are very similar to what you'll see in the actual exam. Recommended!!!
Cassius Aug 10, 2026
Yes, they offer a 100% success guarantee. And many students who have used them have reported passing their exams with flying colors.
Question 21

In the default SD-WAN minimum configuration, which two statements are correct when traffic matches the default implicit SD-WAN rule? (Choose two )

Options:

A.

Traffic has matched none of the FortiGate policy routes.

B.

Matched traffic failed RPF and was caught by the rule.

C.

The FIB lookup resolved interface was the SD-WAN interface.

D.

An absolute SD-WAN rule was defined and matched traffic.

Discussion
Question 22

Questions 22

Exhibit B –

Questions 22

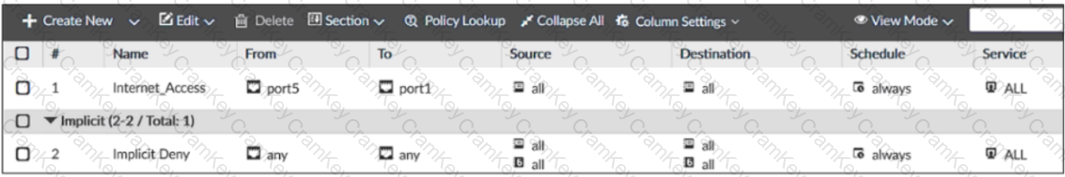
Exhibit A shows the system interface with the static routes and exhibit B shows the firewall policies on the managed FortiGate.

Based on the FortiGate configuration shown in the exhibits, what issue might you encounter when creating an SD-WAN zone for port1 and port2?

Options:

A.

port1 is assigned a manual IP address.

B.

port1 is referenced in a firewall policy.

C.

port2 is referenced in a static route.

D.

port1 and port2 are not administratively down.

Discussion
Question 23

Refer to the Exhibits:

Questions 23

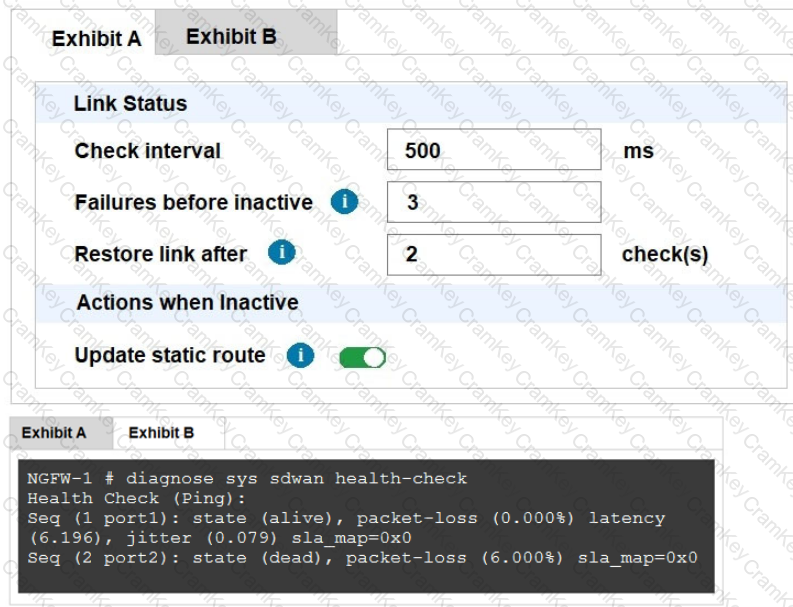
Exhibit A, which shows the SD-WAN performance SLA and exhibit B shows the health of the participating SD-WAN members.

Based on the exhibits, which statement is correct?

Options:

A.

The dead member interface stays unavailable until an administrator manually brings the interface back.

B.

Port2 needs to wait 500 milliseconds to change the status from alive to dead.

C.

Static routes using port2 are active in the routing table.

D.

FortiGate has not received three consecutive requests from the SLA server configured for port2.

Discussion
Page: 5 / 7

NSE7_SDW-7.2
PDF

$31.5  $104.99

NSE7_SDW-7.2 Testing Engine

$37.5  $124.99

NSE7_SDW-7.2 PDF + Testing Engine

$49.5  $164.99